Report Overview
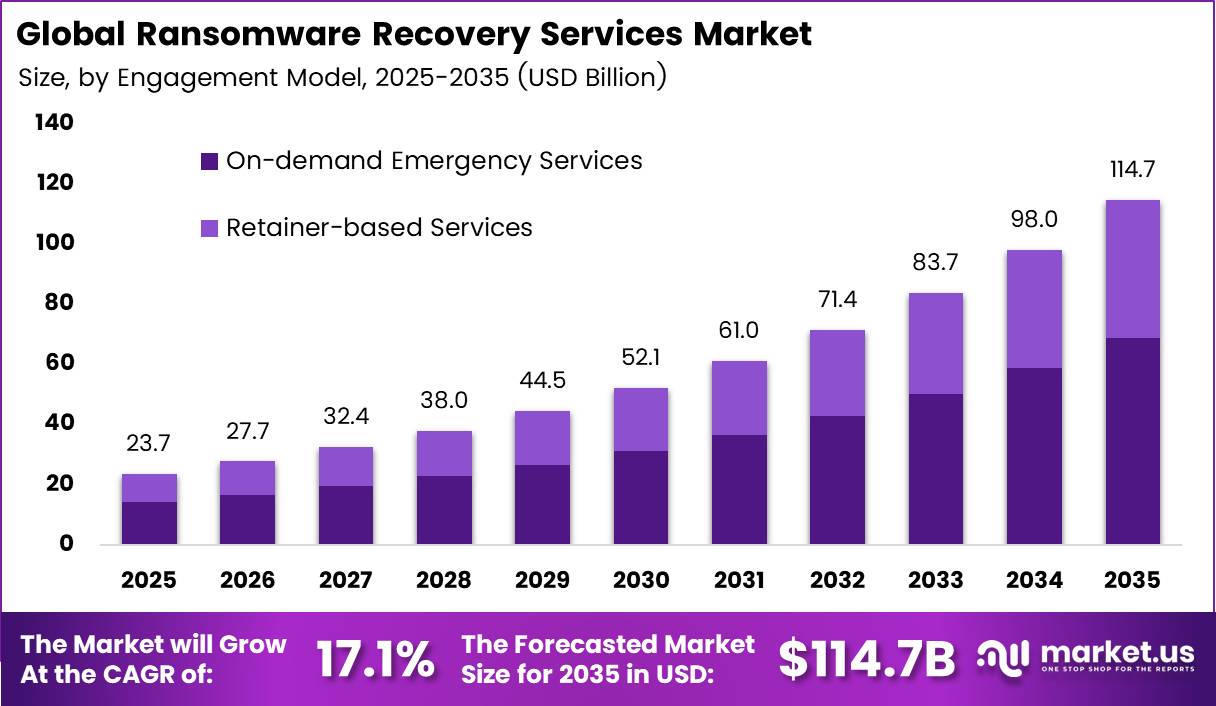
In 2025, the Global Ransomware Recovery Services Market was valued at USD 23.7 billion. The market is projected to grow at a CAGR of 17.1% during 2026–2035, reaching approximately USD 114.7 billion by 2035. North America dominated the global market in 2025, accounting for more than 43.0% of the total market share and generating approximately USD 10.2 billion in revenue.
Rising digital crime drives this demand. According to the FBI Internet Crime Complaint Center (IC3), victims reported 859,532 complaints in 2024, with losses of USD 16.6 billion. That loss total rose 33% from 2023. IC3 named ransomware the most common threat to critical infrastructure, with complaints up 9% in one year.
The North America region has the largest number of reported attacks and the highest spending on response. IC3 logged 263,455 cyber threat complaints in 2024, with USD 1.571 billion in losses. Critical infrastructure groups alone filed 4,878 of these complaints. Akira, LockBit, RansomHub, FOG, and PLAY topped the list of reported variants.
Key Takeaways
- The Ransomware Recovery Services Market reached USD 23.7 billion in 2025 and will reach USD 114.7 billion by 2035. at a CAGR of 17.1% from 2026 to 2035.
- By service type, Data Recovery and Restoration leads with a 28.0% share.
- By engagement model, On-demand Emergency Services lead with a 60.0% share.
- By organization size, Large Enterprises lead with a 65.0% share.
- North America leads with a 43.0% share and USD 10.2 billion in revenue.
By Service Type
Data Recovery and Restoration dominates with 28.0% due to the urgent need to restart operations.
Data Recovery and Restoration leads because every ransomware victim needs its files back before work can restart. The Sophos State of Ransomware 2025 study surveyed 3,400 hit organizations. It found that 97% of firms with encrypted data got that data back. Buyers spend on restoration first because each day of downtime stops sales, payroll, and customer service.
Restoration also comes with heavy bills. Sophos puts the average recovery cost, not counting any ransom, at $1.53 million per attack. Only 54% of victims restored data from backups, the lowest rate in six years. So many firms now hire outside experts to rebuild damaged backups and recover lost records.
Incident Assessment and Digital Forensics grows fastest because attackers change their tools very quickly. The FBI’s Internet Crime Complaint Center found 67 new ransomware variants in 2024. Each new strain forces responders to find out how the attack got in, what data left, and whether threats remain. Insurers and regulators also want proof of the root cause before they close claims.

By Engagement Model
On-demand Emergency Services dominate with 60.0% due to sudden attacks with no plan.
On-demand Emergency Services hold the largest share because most firms only buy help after an attack hits. The FBI received 3,156 ransomware complaints in 2024, and each one marks a crisis that needs fast outside support. Many victims have no plan or vendor ready, so they call emergency teams on day one.
Critical sectors drive much of this urgent demand. The FBI logged 4,878 complaints from critical infrastructure groups. Critical manufacturing alone reported 258 ransomware attacks. Plants and hospitals cannot wait through long contract talks, so they pay for help right away.
Retainer-based Services grow fastest as boards shift from reacting to being ready. Ransomware complaints to the FBI rose 9% in 2023, which pushes firms to sign up response teams before trouble starts. A retainer gives buyers fixed rates, agreed response times, and tested playbooks. Cyber insurers also prefer clients with a signed response partner, which adds to this shift.
By Organization Size
Large Enterprises dominate with 65.0% due to complex networks and high ransom stakes.
Large Enterprises lead because they run complex networks and face the biggest ransom demands. The Sophos State of Ransomware in Enterprise 2025 study puts median ransom demands at $1.20 million. It also shows that 48% of enterprises still paid to get their data back.
Big firms also spend heavily after an attack. Average cleanup costs for enterprises reached $1.84 million. Their use of backups fell to 53%, down from 73% a year earlier. These gaps push large companies to sign multi-service deals that cover forensics, rebuilding, and legal advice.
SMEs are the fastest-growing group as attackers go after easier targets with small IT teams. Sophos data shows that firms with 100–250 employees still face average recovery costs of $638,536, a heavy load for a small budget. Most small firms have no in-house security staff, so they buy recovery as an outside service.
Key Market Segments
By Service Type
- Data Recovery and Restoration
- Incident Assessment and Digital Forensics
- Ransomware Containment and Removal
- System Rebuilding and Operational Recovery
- Cyber-extortion Response and Negotiation
- Post-incident Remediation and Advisory
By Engagement Model
- On-demand Emergency Services
- Retainer-based Services
By Organization Size
- Small and Medium-sized Enterprises (SMEs)
- Large Enterprises
Geopolitical Impact Analysis
Trade tensions shape the cost of the hardware that recovery teams rely on. These teams need servers, storage arrays, and backup appliances to rebuild systems. The WTO reported that world merchandise trade volume grew 4.6% in 2025, well above its earlier forecast of 2.4%. Companies rushed imports into North America ahead of higher US tariffs, and this pushed up demand for data center gear.
That rush created a later dip. The WTO found that North American imports fell 3.2% in the first half of 2026 after the early buying. Recovery firms that stocked spare servers and immutable storage in 2025 kept costs stable. Firms that waited faced tighter supply and higher prices for clean replacement hardware.
The AI investment boom also competes for the same parts. The WTO said AI goods such as semiconductors and processors made up 42% of global trade growth in 2025. Recovery providers buy from the same chip and storage supply chains, so they face long lead times on rebuild hardware. Most of this trade still enjoys low or zero tariffs under the WTO Information Technology Agreement, which has 84 participants.
Policy risk remains high. The WTO noted that about 72% of global goods trade still moves on most-favoured-nation terms, but that share has turned volatile. For 2026, the WTO raised its merchandise trade growth forecast to 3.9% from 1.9%. Any new tariff shock could raise the price of the backup hardware that recovery work needs.
Regional Analysis
North America dominates the Ransomware Recovery Services Market, holding a 43.0% share and generating USD 10.2 billion in revenue. The US drives most of this demand. It hosts the head offices of major platform players such as Google Cloud, Microsoft, CrowdStrike, Palo Alto Networks, and Cisco.
Canada adds steady demand from its public sector and energy firms. The region’s trade picture also shapes hardware supply for rebuild work. The WTO expects North American merchandise imports to grow only 1.4% in 2026. Slow import growth means recovery providers must plan their server and storage stock with care.
Asia Pacific is the fastest-growing region in the market. China, Japan, South Korea, India, and Australia are adding digital infrastructure quickly. The WTO expects Asia to post the strongest import volume growth of any region in 2026, at 9.5%. Much of that growth comes from servers and AI hardware. More connected systems create more targets for ransomware groups.
Europe holds a strong position, and strict rules drive its demand. Germany, France, the UK, Spain, and Italy enforce tough data protection and resilience laws. These laws push firms to keep tested backups and to hire forensic teams after a breach. The WTO expects European imports to grow just 0.5% in 2026, so hardware refresh cycles may slow.

Key Regions and Countries
North America
- US
- Canada
Europe
- Germany
- France
- The UK
- Spain
- Italy
- Rest of Europe
Asia Pacific
- China
- Japan
- South Korea
- India
- Australia
- Rest of APAC
Latin America
- Brazil
- Mexico
- Rest of Latin America
Middle East and Africa
- GCC
- South Africa
- Rest of MEA
Market Dynamics
Drivers
| Driver | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Escalating Ransomware Incident Volume and Variant Diversity | +2.2% | Global, led by North America and Europe | Short term (2 years or less) |
| Mandatory Cyber Incident Disclosure Rules | +1.6% | North America, European Union | Short term (2 years or less) |
| Cyber Insurance Control Requirements | +1.0% | North America, United Kingdom, Western Europe | Medium term (2 to 4 years) |
| Adoption of Immutable Backup and Clean-Room Recovery | +0.8% | Global | Medium term (2 to 4 years) |
| Healthcare and Critical Infrastructure Targeting | +0.7% | North America, Europe, Asia Pacific | Short term (2 years or less) |
| AI-Accelerated Attack Tooling | +0.5% | Global | Medium term (2 to 4 years) |
Escalating Ransomware Incident Volume and Variant Diversity
The root cause is a growing ransomware-as-a-service ecosystem that keeps adding new tooling. According to FBI Internet Crime Complaint Center reporting, ransomware complaints rose to 3,611 in 2025 from 3,156 in 2024, and reported losses grew roughly 259% to above $32 million. The FBI also notes that these figures leave out disruption, recovery, and lost-revenue costs.
Variant diversity is the main lever. IC3 data shows 63 new ransomware variants in 2025, an average of 5.25 per month. Ransomware made up 36% of reported cyberthreats against critical infrastructure, and healthcare took 278 attacks. Each new strain cuts how long decryptors, playbooks, and forensic signatures stay useful. That pushes buyers away from one-off incident fees and toward standing recovery retainers.
The commercial effect is a shift in business model. Sophos enterprise survey data shows backup-based recovery fell to a four-year low of 53% from 73%, while 48% of enterprises still paid ransoms. Vendors are responding by bundling forensics, restoration, and negotiation into annual subscription retainers. This lowers repeat customer acquisition cost and turns episodic revenue into recurring revenue.
Restraints
| Restraint | (~) % Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
|---|---|---|---|
| Declining Per-Incident Recovery Spend | -1.3% | Global | Short term (2 years or less) |
| SME Security Budget Constraints | -1.0% | Asia Pacific, Latin America, Africa | Short term (2 years or less) |
| Sanctions Limits on Ransom Negotiation Services | -0.6% | North America, United Kingdom, European Union | Medium term (2 to 4 years) |
| Data Localization Barriers to Cross-Border Forensics | -0.5% | India, China, Middle East, European Union | Medium term (2 to 4 years) |
| Interest-Rate-Driven IT Procurement Freezes | -0.4% | Global | Short term (2 years or less) |
Declining Per-Incident Recovery Spend
Better backup discipline, stronger ransom negotiation, and coordinated law-enforcement takedowns have shrunk the dollar value of each incident. Sophos enterprise survey data shows median ransom demands fell 56% to $1.20 million from $2.75 million. Mean remediation cost, excluding ransom, dropped to $1.84 million from $3.12 million.
The bottleneck shows up as lower revenue per incident. Sophos global data shows 53% of ransom payers negotiated below the initial demand, and median payments fell about 50% to $1 million. Insurer claims data and FBI Recovery Asset Team activity across 3,900 incidents point the same way: victims are getting more out of each recovery engagement.
Challenges
| Challenge | (~) % CAGR Friction Drag | Geographic Relevance | Mitigation Horizon |
|---|---|---|---|
| Incident Response Talent Shortage | -1.0% | Global | Long term (4 years or more) |
| Unpatched Vulnerability Exploitation Persistence | -0.6% | Global | Medium term (2 to 4 years) |
| Backup Repository Compromise Risk | -0.5% | North America, Europe | Medium term (2 to 4 years) |
| Hybrid Legacy Infrastructure Complexity | -0.4% | Europe, Asia Pacific | Long term (4 years or more) |
| Double Extortion Data Leakage | -0.3% | Global | Medium term (2 to 4 years) |
Incident Response Talent Shortage
The structural weakness is that ransomware recovery depends on scarce skills: forensic analysts, Active Directory rebuild engineers, and backup restoration specialists. In Sophos global survey data, 63% of victims linked their breach to resource constraints, including a lack of cybersecurity expertise or staff.
The friction shows up in timelines. Full operational restoration can take a median of more than 100 days in Sophos data, and forensic and legal work alone can cost between $300,000 and $1.5 million per incident, according to aggregated insurer and vendor cost breakdowns. ISC2 workforce studies show the global cybersecurity workforce gap still runs into the millions.
Opportunities
| Opportunity | (~) % Potential CAGR Upside | Geographic Relevance | Execution Window |
|---|---|---|---|
| SMB Recovery-as-a-Service Subscriptions | +1.6% | Global, led by Asia Pacific and Latin America | Medium term (2 to 4 years) |
| MSP and MSSP Channel Roll-Ups | +1.0% | North America, Europe | Short term (2 years or less) |
| OT and ICS Recovery Services | +0.9% | North America, Europe, Middle East | Long term (4 years or more) |
| SaaS Workload Recovery Coverage | +0.8% | Global | Medium term (2 to 4 years) |
| AI-Automated Forensic Triage | +0.6% | Global | Medium term (2 to 4 years) |
SMB Recovery-as-a-Service Subscriptions
This is still white space, not a current driver. Today’s recovery spend is concentrated among enterprises with retainers and insurance panels, while small businesses mostly buy help reactively, or not at all. Sophos data shows median demand for smaller firms at around $350,000, compared with $5 million for organizations with revenue above $1 billion.
The unit-economics case rests on standardization. FBI IC3 data puts the average cybercrime loss at $20,699 across more than 1 million complaints, which fits a low-ticket, high-volume subscription model better than bespoke engagements. Templated restoration playbooks and pooled immutable storage could reduce delivery cost per client by roughly 30% to 40%.
Capturing this requires deliberate channel building through managed service providers and regional distributors. If successful, gross margins could expand by about 8 to 12 percentage points over project-based incident response, turning unmet demand into recurring annual contract value.
Key Players Analysis
Tier 1 leaders combine large platforms with incident response teams. Google Cloud made the biggest move in the sector. It closed its USD 32 billion all-cash purchase of Wiz in March 2026. US regulators cleared the deal in November 2025, and EU regulators followed in February 2026. Wiz now adds cloud security to the Mandiant response business inside Google Cloud.
Palo Alto Networks completed its largest deal ever in February 2026. It bought CyberArk for about USD 25 billion, paying USD 45.00 in cash plus 2.2005 shares for each CyberArk share. The deal adds identity security to its Unit 42 response unit. Stolen credentials often open the door to ransomware, so this pairing matters for recovery work.
CrowdStrike posted total revenue of USD 1.23 billion in Q3 of fiscal 2026, up 22% from a year earlier. Subscription revenue reached USD 1.17 billion. The company spent USD 347.6 million on research and development in that quarter and USD 1.03 billion across the first nine months. Microsoft, IBM, Cisco, Sophos, Rapid7, and SentinelOne also sit in Tier 1. Each pairs its detection tools with response retainers.
Tier 2 challengers hold strong niche positions. Veeam leads in backup and data restoration. It paid USD 1.725 billion for Securiti AI in a deal that closed in December 2025, and it expects close to USD 2 billion in annual recurring revenue. Kroll, Arete, S-RM, Quorum Cyber with Kivu, and KLDiscovery focus on forensics, negotiation, and legal support after an attack.
Top Key Players in the Market
- Google Cloud
- CrowdStrike
- Palo Alto Networks
- Microsoft
- IBM
- Kroll
- Sophos
- Cisco
- Rapid7
- SentinelOne
- Veeam
- Arete
- S-RM
- Quorum Cyber, including Kivu
- KLDiscovery
Recent Developments
- In March 2026, Google completed its USD 32 billion all-cash purchase of Wiz and moved the cloud security platform into Google Cloud.
- In February 2026, Palo Alto Networks completed its roughly USD 25 billion purchase of CyberArk and made identity security a core part of its platform.
- In October 2025, Veeam signed a deal to buy Securiti AI for USD 1.725 billion to join data recovery with data security posture management.
Report Scope
| Report Features | Description |
|---|---|
| Market Value (2025) | USD 23.7 Billion |
| Forecast Revenue (2035) | USD 114.7 Billion |
| CAGR (2026-2035) | 17.1% |
| Base Year for Estimation | 2025 |
| Historic Period | 2020-2024 |
| Forecast Period | 2026-2035 |
| Report Coverage | Revenue Forecast, Market Dynamics, Competitive Landscape, Recent Developments |
| Segments Covered | By Service Type (Data Recovery and Restoration, Incident Assessment and Digital Forensics, Ransomware Containment and Removal, System Rebuilding and Operational Recovery, Cyber-extortion Response and Negotiation, Post-incident Remediation and Advisory); By Engagement Model (On-demand Emergency Services, Retainer-based Services); By Organization Size (Small and Medium-sized Enterprises (SMEs), Large Enterprises) |
| Regional Analysis | North America – US, Canada; Europe – Germany, France, The UK, Spain, Italy, Rest of Europe; Asia Pacific – China, Japan, South Korea, India, Australia, Singapore, Rest of APAC; Latin America – Brazil, Mexico, Rest of Latin America; Middle East & Africa – GCC, South Africa, Rest of MEA |
| Competitive Landscape | Google Cloud, CrowdStrike, Palo Alto Networks, Microsoft, IBM, Kroll, Sophos, Cisco, Rapid7, SentinelOne, Veeam, Arete, S-RM, Quorum Cyber, including Kivu, KLDiscovery |
| Customization Scope | Customization for segments and region/country-level will be provided. Moreover, additional customization can be done based on the requirements. |
| Purchase Options | We have three licenses to opt for: Single User License, Multi-User License (Up to 5 Users), Corporate Use License (Unlimited Users and Printable PDF) |